
Troubleshooting
Social media oversharing can turn your digital life into a privacy disaster. These 10 real-life stories reveal how innocent posts can lead to identity theft, stalking, job loss, and more - with lessons to protect yourself now.
Vacation home robbery from Instagram posts
A family’s three-week vacation turned into a nightmare when Instagram posts revealed their empty home—leading to a targeted robbery. Criminals used location tags and check-ins to confirm the house was vacant, demonstrating how seemingly harmless posts create security blind spots.
The geotagged photos of their beach trip and airport check-ins gave thieves precise timing for the break-in. Even "private" stories can be screenshotted or accessed by unauthorized users, turning your digital footprint into a real-world security risk. This case highlights why automatic location services and public posts should be disabled before travel.
Homeowners and frequent travelers should treat social media like an open door—one click can invite trouble. Always review privacy settings and disable location sharing when away. 🔧
Facebook posts leading to job termination
A single offensive Facebook comment from 2018 didn’t just resurface—it derailed a career. When a mid-level manager’s archived political rant resurfaced during a promotion review, HR had no choice but to terminate him, citing "misalignment with company values." This case proves that even deleted posts can linger in cached archives or screenshots.
Many assume posts disappear after deletion, but Facebook’s "View As" privacy tool and third-party archives (like the Wayback Machine) preserve content indefinitely. A 2022 LinkedIn survey found that 63% of HR professionals screen candidates’ social media—meaning a single old post could cost you a job years later. The lesson? Assume nothing is truly private.
This scenario hits hardest for professionals in corporate, government, or client-facing roles, where perception is everything. If your job hinges on trust, treat social media like a permanent résumé—one that could be audited at any time. 💻
Stalking enabled by exact daily routines
Your daily gym check-ins and coffee shop selfies might seem harmless—but they could be painting a target on your back. A stalker used geotagged posts to track a victim’s predictable routine, showing how even "innocent" location services reveal dangerous patterns when combined.
Apps like Instagram, Strava, and Snapchat automatically log your movements, creating a digital breadcrumb trail. A stalker exploited consistent timing (e.g., 6 AM gym, 10 AM coffee) to time harassment, proving that oversharing isn’t just about privacy—it’s about personal safety. Even "private" stories can be screenshotted or leaked.
This isn’t just a theoretical risk—it’s a real tactic used by predators. If you’re active on fitness or lifestyle apps, disable location services for posts and review your activity history regularly. Your routine should stay private. ✨
Medical identity theft from hospital selfies
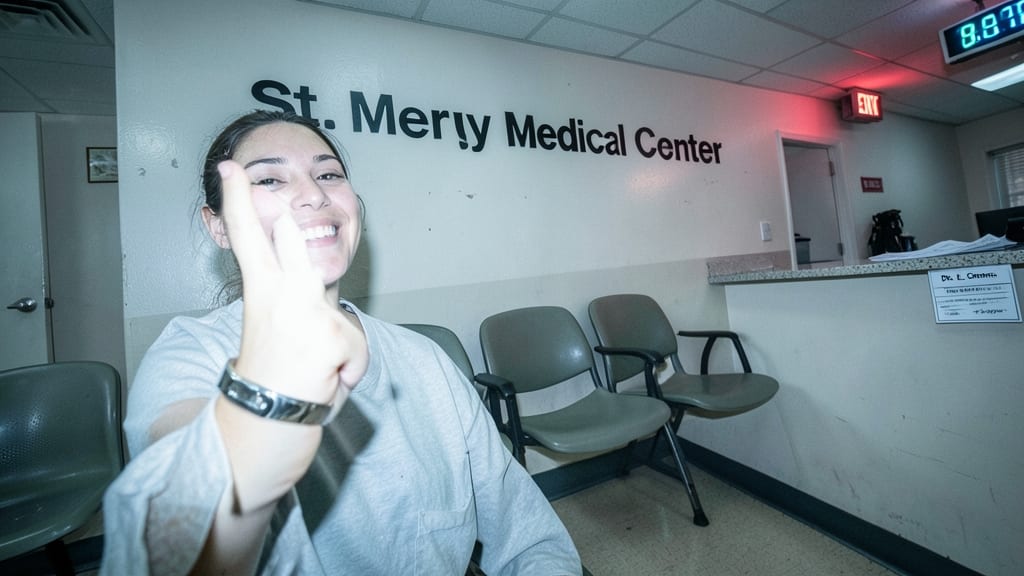
A single selfie in the ER waiting room became a goldmine for identity thieves when a patient unknowingly exposed her hospital name, treatment details, and even insurance provider in the background. Fraudsters used this information to file fake claims under her name, costing her thousands in denied payments and credit damage.
Unlike location-based oversharing, this case highlights how metadata in photos—like hospital signage, medical equipment, or even staff uniforms—can reveal sensitive information. Even cropping the photo doesn’t remove embedded data; thieves can extract details from the original file. The victim’s social media privacy settings were already strict, proving that oversharing isn’t just about what you post, but what’s visible in your posts.
Anyone who’s ever posted from a hospital, clinic, or even a doctor’s office should audit their photo libraries for hidden details. Use tools like EXIF viewers to check for embedded data before sharing. 💻
College admission rejection from party photos
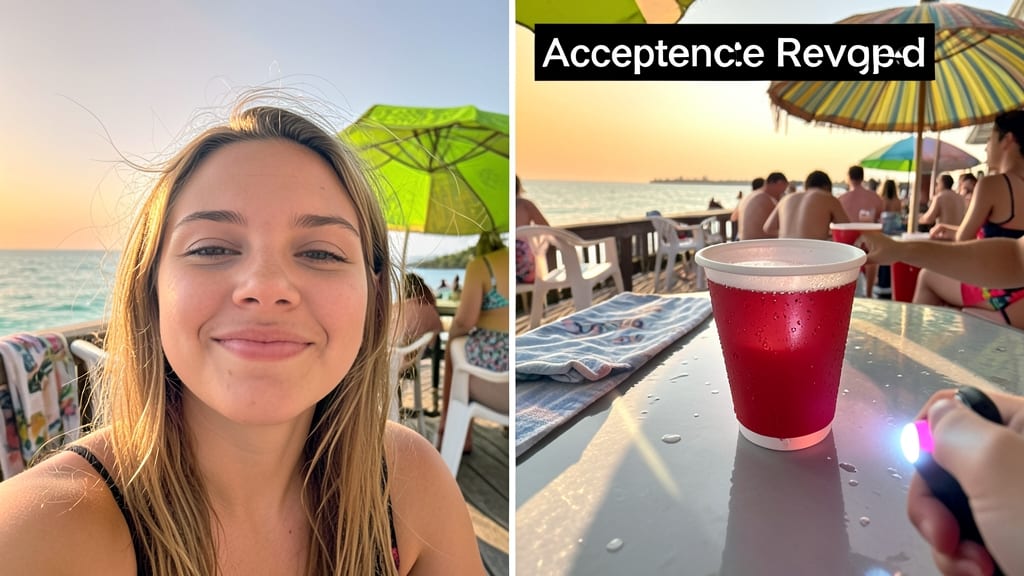
A high school senior’s spring break photos of underage drinking didn’t just disappear—they became a red flag for her dream university’s admissions team. While scrolling through her public Instagram posts, recruiters spotted the photos and immediately rescinded her acceptance, citing a violation of the school’s community standards policy.
Many universities now use social media screening tools like Social Intelligence or HireVue to cross-reference applicants’ online activity with their stated values. Even private accounts can be accessed if they’re linked to a school email or shared with friends who post publicly. The lesson? One risky photo can override years of academic achievements—and digital footprints last forever.
Students applying to competitive programs should treat social media like a background check. Use platform privacy settings (e.g., Instagram’s “Close Friends” lists, LinkedIn’s “Profile Visibility”), and avoid tagging locations or people in posts that could be misconstrued. A simple audit before submission could save your future. ✨
Financial scams using personal life events
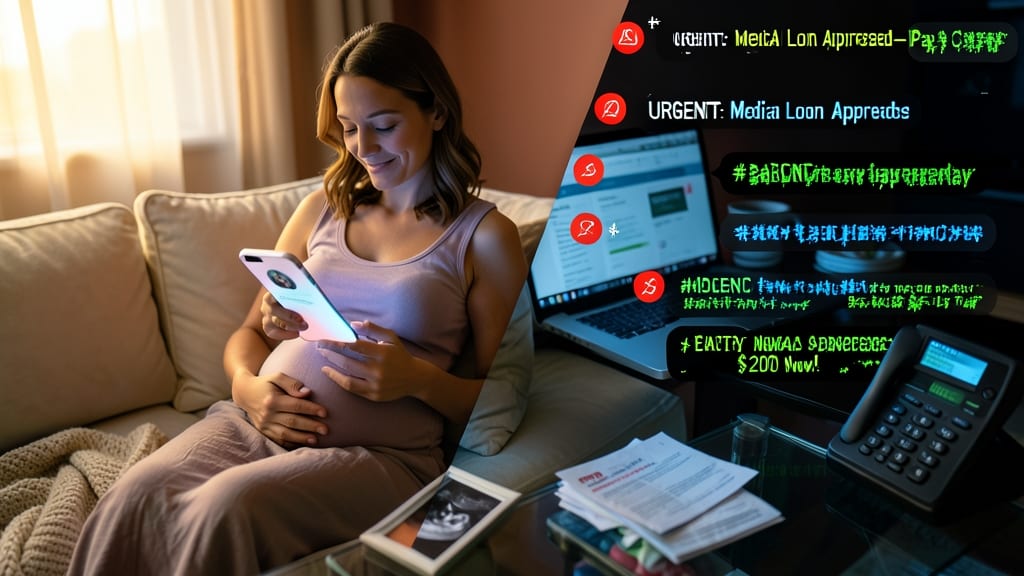
Celebrating a pregnancy should be joyful—but one expectant mother’s announcement triggered a wave of targeted financial scams. Within hours of posting her news, she received calls and texts offering "exclusive" loans for medical expenses, followed by demands for upfront fees. Scammers also posed as medical equipment suppliers, pressuring her to pay for "urgent" supplies she never ordered.
These schemes exploit emotional vulnerability during life milestones, using fake urgency (e.g., "limited-time offers") and personal details (like due dates) to bypass skepticism. The FTC reports a 40% increase in pregnancy-related financial fraud since 2022, with victims losing an average of $2,500 before realizing they’ve been scammed. Even seemingly harmless updates—like wedding plans or new jobs—can attract similar predatory tactics.
Parents-to-be and anyone announcing major life changes should freeze accounts temporarily, verify all unsolicited offers, and enable two-factor authentication on financial platforms. Scammers count on excitement clouding judgment—staying sharp is your best defense. 💡
Divorce case strengthened by social media evidence
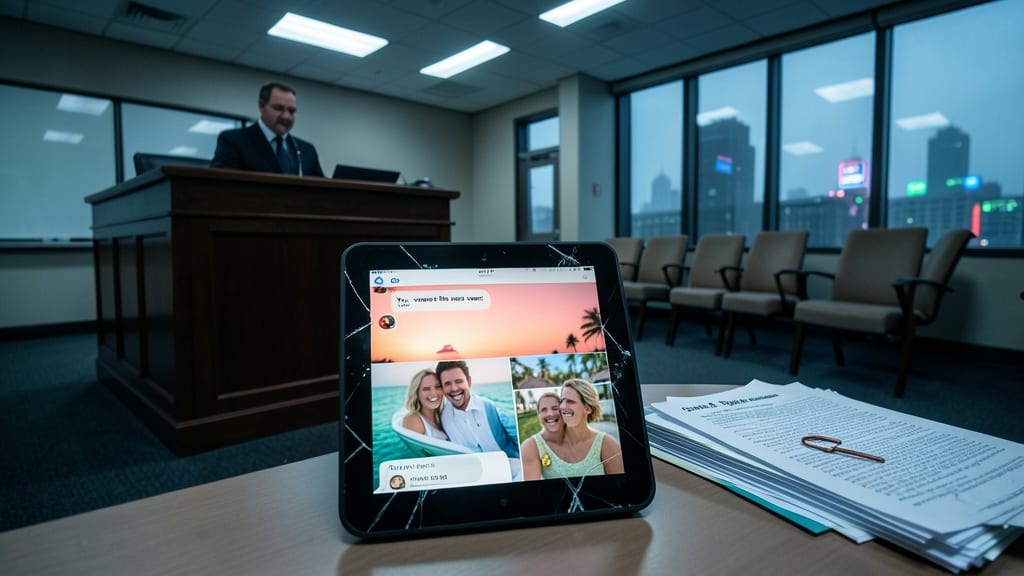
A divorce case that could’ve been settled privately exploded into a public spectacle when screenshots of DM arguments and vacation photos with other partners surfaced in court. What started as private conversations became admissible evidence, proving how easily digital footprints can dismantle relationships—and wallets.
Legal teams now routinely request access to social media metadata, including deleted messages and geotagged photos. A 2023 study found that 68% of divorce cases involving digital evidence saw longer court battles and higher settlements. Even "private" stories on Instagram or Snapchat can be subpoenaed, turning emotional moments into legal ammunition.
If you’re in a high-conflict relationship or co-parenting, assume nothing is truly private. Enable end-to-end encryption for DMs, review app permissions, and consider a digital detox during separations. 💻
Kidnapping attempts from school location posts
Think sharing your child’s school drop-off photo is harmless? That geotagged location could turn into a predator’s treasure map. One mother’s daily posts of her son’s bus stop became a pattern predators exploited to track his routine—leading to multiple attempted abductions outside the school gates.
Most smartphones auto-tag photos with GPS coordinates unless disabled, and even "private" posts can be screenshotted or scraped. Predators use tools to map routines from public profiles, turning predictable patterns (like after-school soccer practice) into opportunities. Schools and law enforcement now warn parents that one photo per week—without exact timing—is far safer than daily updates.
Parents of school-age kids should disable geotagging in camera settings, avoid posting real-time drop-off photos, and use apps like Google Photos’ "Location History" to scrub old metadata. The cost of a moment’s pride? Your child’s safety. ⚡
Military deployment compromised by status updates
A single "I'm safe!" status update from a deployed soldier didn’t just boost morale—it became a tactical blueprint for enemies. In a documented case, a U.S. military unit’s daily location check-ins on social media revealed exact deployment timelines, allowing adversaries to launch coordinated ambushes with surgical precision.
The problem wasn’t just the posts themselves—it was the metadata hidden in timestamps, GPS tags, and even seemingly harmless emoji reactions. One soldier’s "Heading to the FOB" update, paired with a geotagged photo, gave enemies a real-time advantage, turning what should have been a secure operation into a high-risk scenario. Even encrypted messages can be intercepted if shared publicly.
This isn’t just a military issue—anyone sharing location data (even "just" for family updates) risks exposing routines to the wrong eyes. For service members, the stakes are life-or-death, but for civilians, the lesson is clear: Assume nothing is private online. ✨
Blackmail attempts from private messages
You might assume direct messages (DMs) are private—but cybercriminals exploit even the most casual conversations to build psychological leverage. A single venting session about financial stress, relationship troubles, or medical issues can be weaponized into a blackmail scheme, with attackers threatening to expose your secrets unless paid.
These scams often start with fake profiles posing as friends, romantic interests, or even employers, then escalate by recording voice notes or screenshots of your DMs. Victims report demands ranging from $500 to $5,000, with attackers exploiting emotions like guilt or fear. Unlike public posts, DMs leave no audit trail—once sent, they’re out of your control.
This tactic preys on highly personal topics (e.g., infidelity, debt, or health crises), making it harder to recover. Even encrypted apps like Signal aren’t immune—attackers may use social engineering to trick you into sharing sensitive details first. 💻